
mSecure Support
Important Security Notice 2026-11-03
mSecure support. Here's an idea to help. I expect management are dragging their feet on an announcement for damage limitation but what would be helpful is to at least offer this.
* Is the email we received genuine? Just confirming that would be helpful.
* Is it source code, access logs, disclosure or a triggered canary that has caused this alert?
* If it isn't compromised code, is it safe to open the app so we can change our passwords???
Basically at the moment this might be email is hacked and is just a storm in the teacup. Alternatively it might be catastrophic. No updates assumes catastrophic breach.
Could it be that only their email system was compromised and someone sent out a bogus communication claiming there had been a breach?
I tried running the text of their email through a couple of AI content detectors. Here's what ZeroGPT and HumaLingo had to say about it.
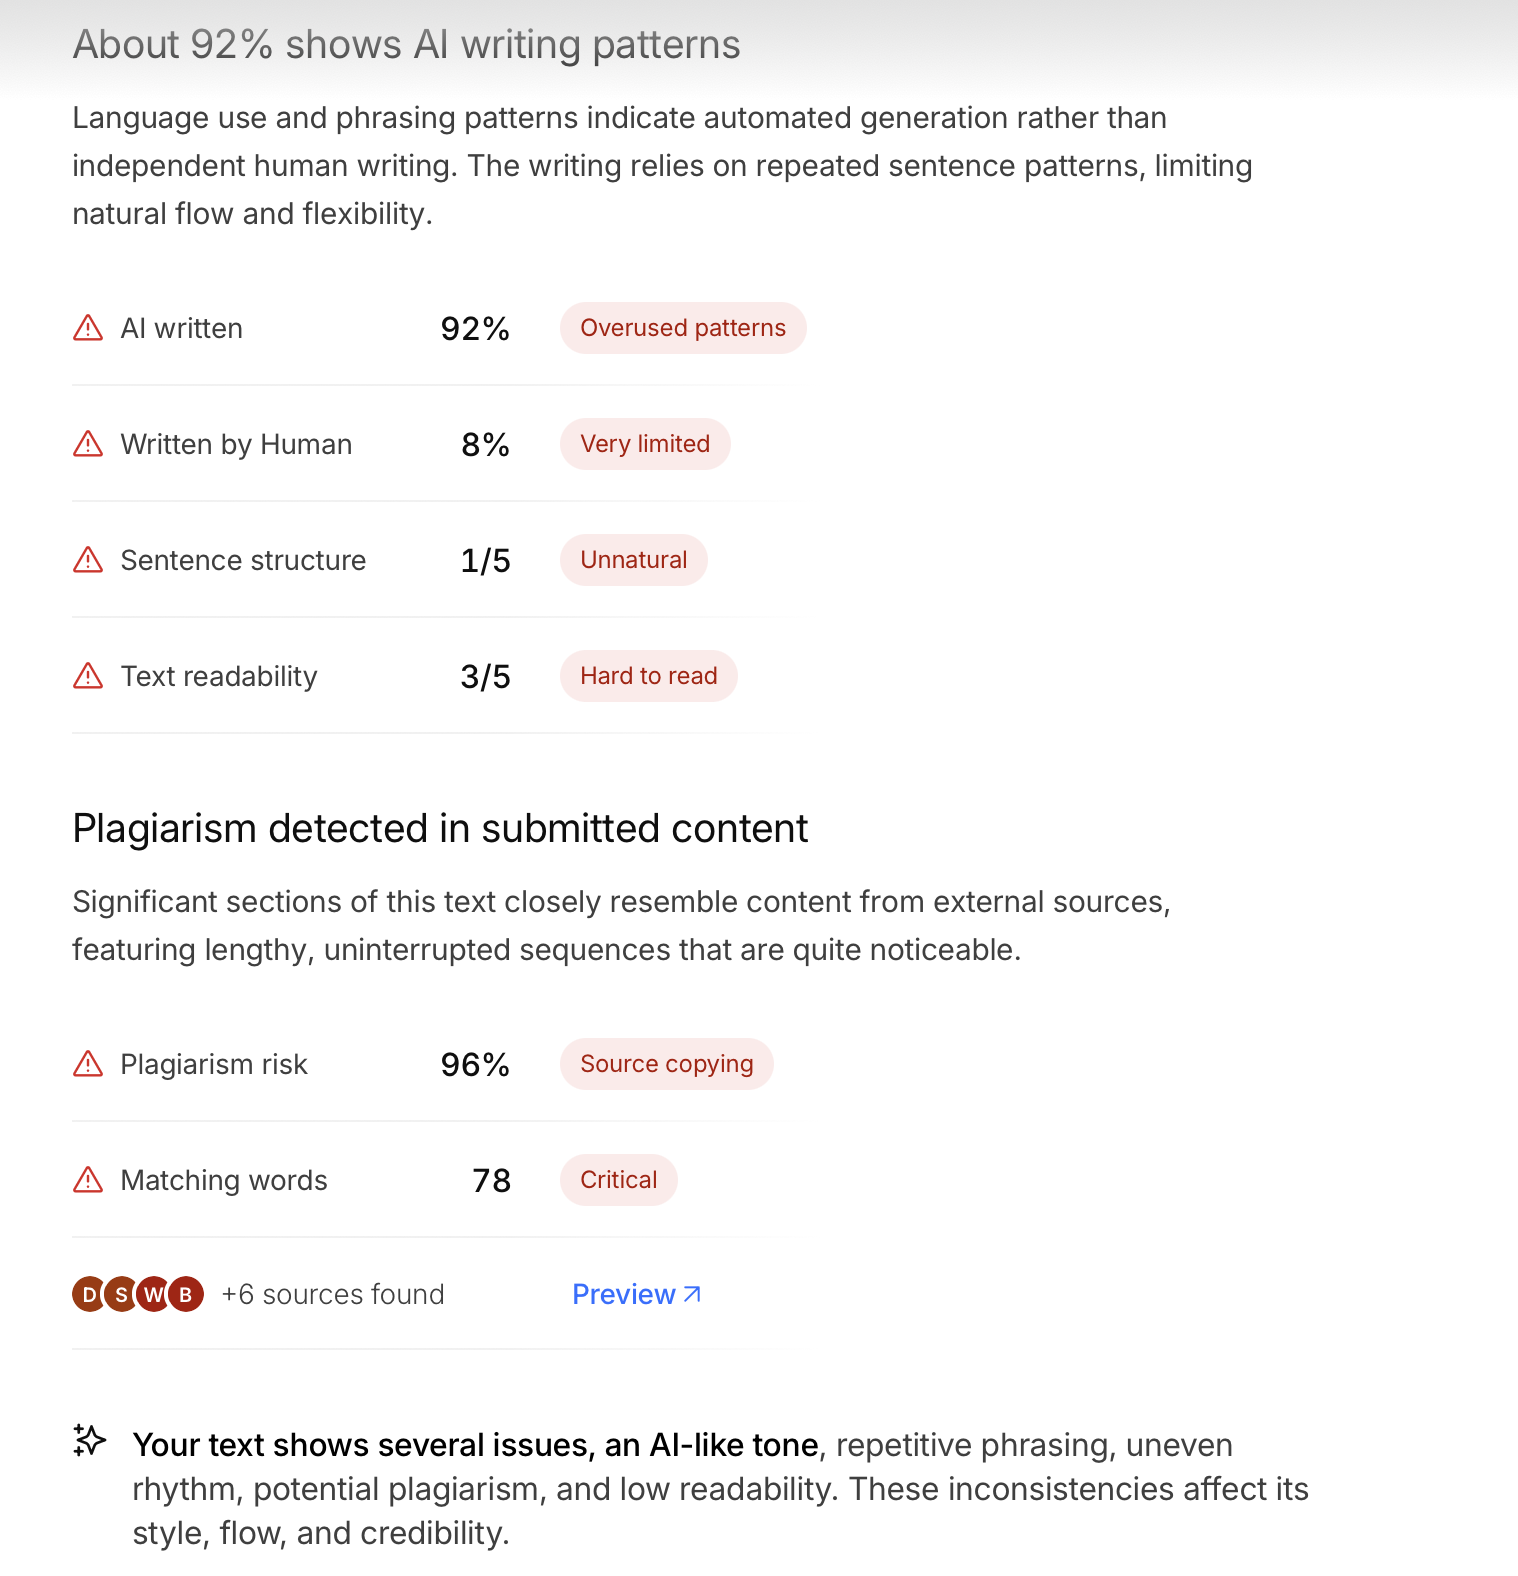
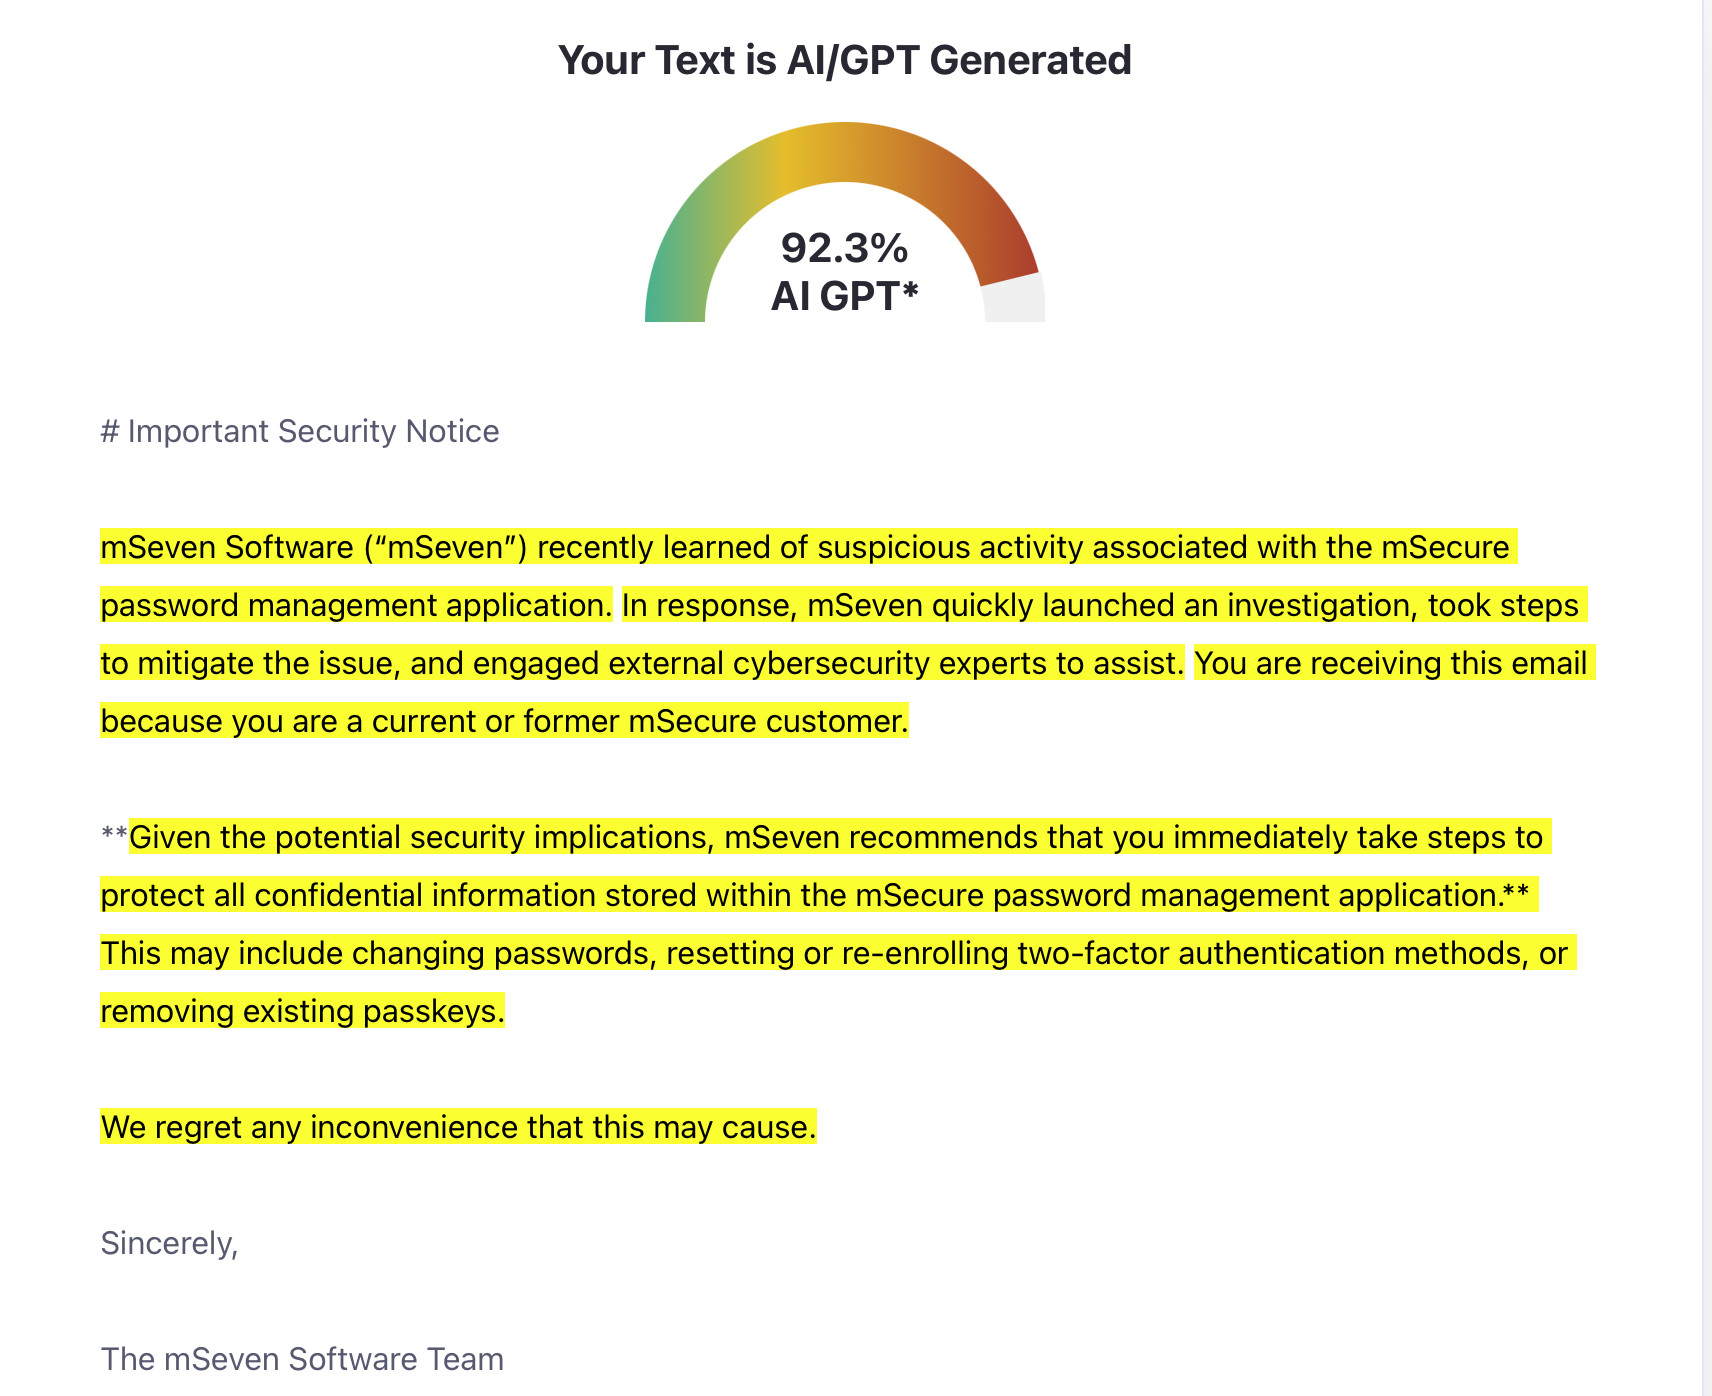
It is more than obvious that there has been a security incident. If there had not been one, mSeven would presumably have issued a clear denial by now, particularly given the large number of posts on the matter.
Why is there no response? One possible explanation is that the situation is more serious than they are currently prepared to acknowledge. The continued lack of communication certainly suggests to me that they are simply not in a position to provide clear answers at this point.
Speculating now about whether the wording of the email may have been AI-generated is not helpful in the slightest.
At the end, it does not matter to me whether this email written by them - or not.
If this was unintended, they failed in keeping their own system safe.
Even worse is their response to this event.
Dozens of questions and no replies.
Such application demands trust, and my trust on them is now gone.
You're probably right and a security incident seems highly probable, which would be a nightmare. As a glimmer of hope, could it be that they're not responding because it's still outside their working hours? mSeven seems to be based in Lake Oswego, OR, where it's currently 7 in the morning. Yes, that would be absurd, but still...
According to msecure's own information
"With zero-knowledge architecture, only you can access your data – not even mSeven Software can access it, since we do not store your account password or account key on our servers. Cloud and Wi-Fi sync, backup and recovery, biometric unlock, and auto-lock settings ensure complete protection across all your devices."
How could there be a breach that exposes our data unless secure is lying to us about security - WE NEED MORE INFO!
Once again my words regarding this, in the main topic about it:
This is an extremely unprofessional action of msecure. If indeed it is true that someone with malicious intentions was able to break in an app running on unmodified iOS, iPadOS or macOS that is breaking world news. We are extremely worried because there is no information at all about what PRECISELY happened. We store hundreds of passwords in the app, for obvious reasons ONLY running local. No cloud back-ups, no msecure online. Besides, there are also credicards, passports nd many more extremely privacy sensitive data stored within this app. If that all must be replaced, we assume the bills can be send to msecure?
In essence as long as msecure not informs us clearly about what happened, how it happened and who is affected it spunds wise to remove this app from all systems. All alarmbells went off here, both private and business wise.
WE HAVE THE RIGHT TO KNOW WHAT IS GOING ON. A mail with instructions to simply change all passwords, pincodes (not even possible) etc is ridiculous.
The deafening silence is extremely worrying, maybe this is a one-person company??? Unacceptable and a potentially very costly joke. Time to move to another solution, don’t trust this at all anymore.
We certainly do need to know more. One issue that pops to mind beyond what I've read above is that I received an mSecure app update on my iPhone on October 31st (3 days ago). If this update distributed a hacked copy of mSecure, Everyone needs to know this now.
Can msecure clock in here? Urgently needed!!! The costs involved here could be monumental if indeed the local password database was compromised. That would be unheard of anyway. We seem to be in very big trouble!
The question from Hans-Josef is worth checking:
https://support.msecure.com/de/support/discussions/topics/36000038892
In his question, he includes this audit finding:
"Technical information is sent to the manufacturer, allowing them to access the contents of the password manager."
Just triaged my entries in mSecure.
Approx. 800 entries. Quite some are irrelevant. But the total number of relevant ones including those with API-Keys, personal documents like ID-Card, Credit Cards Details, Passwords is still above 600 entries.
When you start to think about what can be deprioritized, you realize that pretty much everything is of high importance. Changing API keys on Cloudflare can be done easily - ok, it takes a while until everything is up and running again. VPN keys on multiple machines. VPN keys authorizing routers to build cross site VPN.
And? Where shall I store them without any information? mSecure is compromised unless I don't get further information. So, I can't even start doing anything, but closing down critical services, closing the firewall and stopping everything that is (was) working seamlessly.
Security incidents can happen. But no communication is what makes things even worse.
The silence is making this worse. Please at least confirm that the email is legitimate and tell us whether Dropbox-sync, iCloud or which users are affected. Asking customers to replace hundreds of credentials without explaining the risk is unacceptable.
Barb
I opened a ticket. I am not sure if they are even thinking of looking at this chat. I recommend that everyone open a ticket and tell them to get on and respond to this thread.
Any official announcement?
@Vilnius Yes, we all should change our passwords, block scanned cards, ID’s etc. As far as the vague msecure message is concerned, all is compromised.
What we URGENTLY need now is an export tool that makes a pdf or so with ALL data including scanned documents etc. Even better a universal database format that can be imported in any other safe password manager or database application. Unfortunately, msecure can import many file formats, but export nothing.
Matthew
This seems ominous:
Given the potential security implications, mSeven recommends that you immediately take steps to protect all confidential information stored within the mSecure password management application. This may include changing passwords, resetting or re-enrolling two-factor authentication methods, or removing existing passkeys.
500+ passwords, lot of changing. This will require a triage.
re-enrolling two-factor authentication methods? just for msecure, or every account referenced within msecure?
all passkeys that I use?
all passkeys that I use on devices that has msecure installed?
just the passkey to access msecure?
If I perform these recommendations, and use the current version of msecure to manage these changes, what risks are the security implications?
32 persone hanno questa domanda